

Protect Your Customer Info with Expert CRM Migration
Why Security is Non-Negotiable in CRM Migration
A secure CRM data migration is essential for protecting your customer information during the transition to a new system. To migrate your data safely, you need a structured approach that includes data auditing, encryption during transfer, access controls, thorough testing, and ongoing monitoring. Microsoft Dynamics 365, implemented by BeyondCRM, provides enterprise-grade security features that protect your data throughout the migration process.
Customer data is one of your most valuable business assets. When you’re moving from spreadsheets, outdated systems, or another CRM to Microsoft Dynamics 365, every piece of customer information needs protection.
A single security lapse during migration can expose sensitive data, damage customer trust, and result in regulatory penalties. According to research, poor data quality alone costs organisations an average of $12.9 million annually, and this risk multiplies when data is in transit between systems.
The good news? With the right approach, you can migrate your CRM data securely while maintaining business continuity. This means planning ahead, implementing proper encryption, controlling who accesses your data, and validating everything after the move.
Think of it like moving house with valuable items. You wouldn’t just throw everything in a truck and hope for the best. You’d plan carefully, use proper packaging, track your belongings, and verify everything arrived safely. Your customer data deserves the same level of care.
I’m Warren Davies, and I’ve led secure CRM data migrations for over 30 years, specialising in Microsoft Dynamics 365 and helping businesses of all sizes protect their customer data during transitions. At BeyondCRM, Secure CRM data migration is built into every project we deliver, from initial planning through to post-migration support.
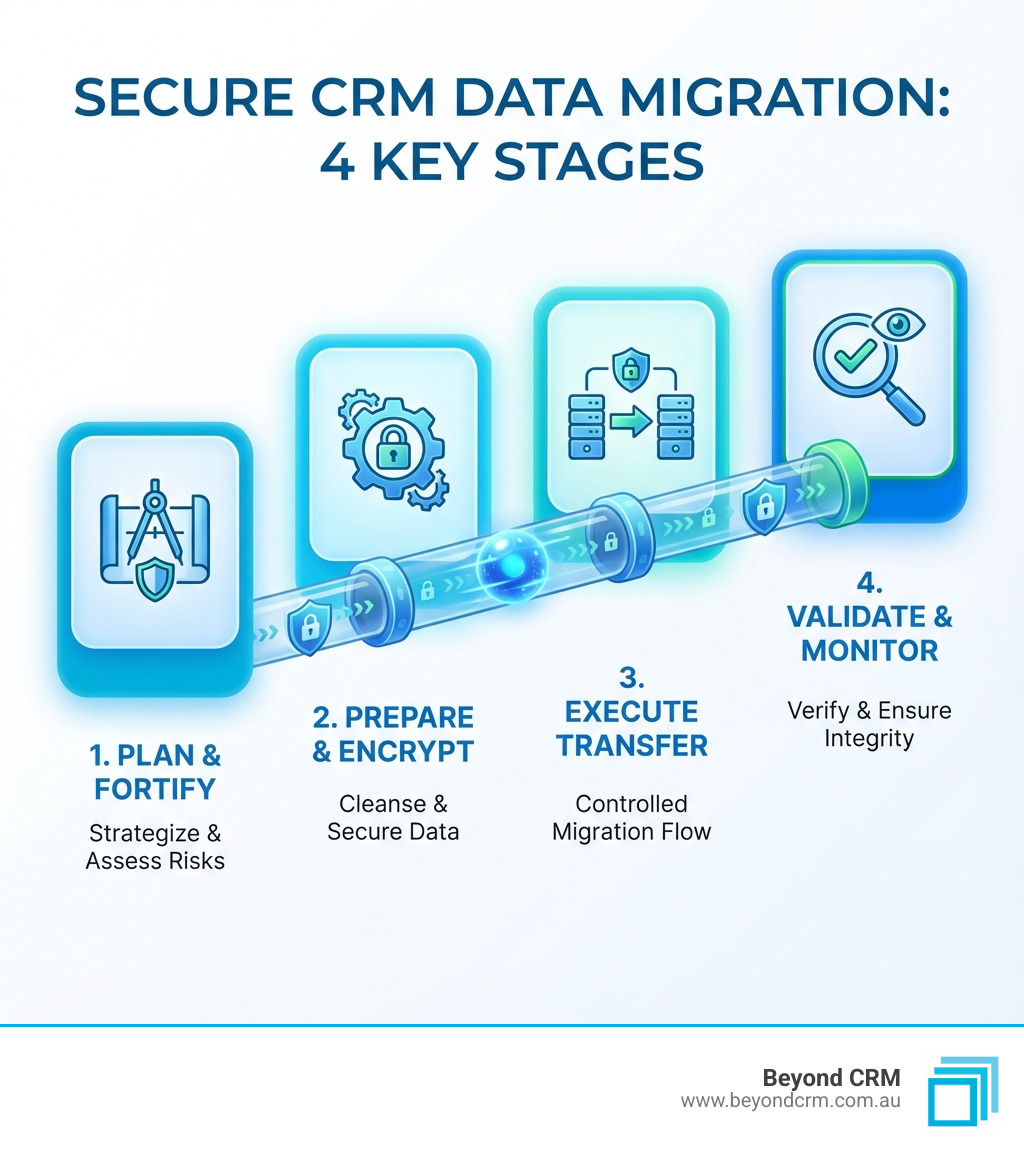
The Blueprint for a Secure CRM Data Migration
This section outlines BeyondCRM’s proven process for keeping your data safe when moving to Microsoft Dynamics 365. We combine industry best practices with our deep expertise in Dynamics 365 to deliver a migration that is both efficient and secure. Our methodology ensures that your customer data, the lifeblood of your business, is handled with the utmost care and precision.
Phase 1: Planning, Fortification, and Risk Assessment

The foundation of any secure migration is meticulous planning. In this phase, we work closely with your team to understand your data landscape and establish a robust security framework. Our strategic consulting helps us identify potential challenges and implement safeguards from the outset.
- Data audit and quality review: Before we move anything, we conduct a thorough audit of your existing data. This helps us identify inconsistencies, redundancies, and outdated information. Considering that over 70% of CRM records can become inaccurate within a year, a comprehensive review is crucial to avoid migrating “garbage in, garbage out.”
- Data cleansing and scope definition: We help you clean your data by removing duplicates, standardising formats, and updating stale records. This also involves defining what data needs to be migrated, what can be archived, and what should be discarded. We often apply a ‘Keep-Clean-Archive’ framework, ensuring only valuable, active, and compliant data makes the journey.
- Identifying risks and compliance checks (e.g., GDPR, Australian Privacy Principles): We assess potential security risks inherent in your source system and the migration process itself. This includes identifying vulnerabilities in migration tools and processes. We also ensure strict adherence to data protection regulations like the Australian Privacy Principles (APP), which are vital for businesses operating in Australia. Compliance is not just a checkbox; it’s a commitment to protecting your customers’ privacy. Learn more about Australian Privacy Principles
- Data mapping for Dynamics 365: Our experts carefully map your existing data fields to their corresponding locations within Microsoft Dynamics 365. This step is critical for data integrity and ensuring that all information flows correctly into your new system. We pay close attention to preserving relationships between records, such as contacts linked to companies or opportunities.
- Encryption in transit (TLS) and at rest (AES): Data security is paramount throughout the migration. We ensure that data is encrypted both when it’s moving between systems (in transit) using protocols like Transport Layer Security (TLS), and when it’s stored (at rest) using strong encryption standards like Advanced Encryption Standard (AES). This protects your sensitive information from unauthorised access at every stage.
- Role-based access control (RBAC) and multi-factor authentication (MFA): Access to your data during migration is strictly controlled. We implement Role-Based Access Control (RBAC) to ensure that only authorised personnel can access specific datasets, and only for the duration of the migration. Multi-Factor Authentication (MFA) adds an extra layer of security, verifying user identities before granting access.
- BeyondCRM’s strategic consulting ensures your migration is secure from the start: Our strategic consulting services are designed to address your unique business needs, ensuring that security is integrated into every aspect of your migration plan. We partner with you to develop a custom solution that minimises risk and maximises efficiency.
More info about our strategic consulting services
Phase 2: Testing and Executing the Secure CRM Data Migration
Once the planning is complete, the next crucial step is to test the migration process thoroughly before moving live data. This iterative approach allows us to refine our methods and ensure a seamless transition.
- Test migrations using dummy data in a secure staging environment: We never migrate your live data without extensive testing. We perform multiple dry runs using dummy data in a secure, isolated staging environment that mirrors your new Dynamics 365 setup. This helps us ensure the migration tool works as expected, identify any potential issues, and adjust protocols without risking your actual customer information. As one expert noted, running multiple tests with dummy data is crucial for ensuring the migration tool is flawless and for monitoring for data leaks before touching live data.
- Data integrity checks and vulnerability testing: During testing, we rigorously check for data integrity, ensuring that all migrated data is accurate, complete, and consistent. We also conduct vulnerability testing to identify and mitigate any security weaknesses in the migration pathway or the new system configuration.
- User Acceptance Testing (UAT) with your team: Your team knows your data best. We involve key users in User Acceptance Testing (UAT) to validate the migrated data and processes. This ensures that the new Dynamics 365 environment functions as expected for your daily operations and that all business-specific requirements are met. Client involvement in testing is vital for identifying gaps related to specific business needs.
- Choosing the right migration approach (e.g., staged or all at once): Depending on the volume and complexity of your data, we help you choose the most appropriate migration strategy. A ‘Big Bang’ approach migrates all data at once, suitable for smaller datasets. For larger or more complex migrations, a ‘Trickle’ or phased approach, moving data in stages, can minimise disruption and allow for continuous validation.
- Managing downtime and live data transfer: We carefully plan the live data transfer to minimise downtime and ensure business continuity. Our team works to schedule the migration during off-peak hours where possible, ensuring your operations are minimally impacted.
- Real-time monitoring and audit logs for full visibility: During the actual migration, we employ real-time monitoring tools to track data movement and system performance. Comprehensive audit logs provide full visibility into the process, allowing us to identify and respond to any anomalies or potential security incidents promptly.
- BeyondCRM’s expert team guides you through every step: Our experienced professionals are with you throughout the execution phase, providing hands-on support and expertise. We leverage our deep knowledge of Microsoft Dynamics 365 to ensure a smooth and secure transition.
Learn more about secure data migration best practices from Microsoft
Phase 3: Post-Migration Validation and Ongoing Governance
The migration isn’t over once the data is in your new Dynamics 365 system. This final phase focuses on confirming the success of the migration, establishing ongoing security practices, and empowering your team.

- Post-migration validation to confirm data accuracy: Immediately after migration, we perform a final, comprehensive validation to confirm that all data has been accurately transferred and is fully functional within Dynamics 365. This includes verifying record counts, checking data relationships, and ensuring reporting functions correctly.
- Ongoing monitoring and regular security audits: Security is a continuous process, not a one-time event. We help you establish ongoing monitoring protocols and recommend regular security audits for your new Dynamics 365 environment. This proactive approach helps detect and address new threats or vulnerabilities as they emerge.
- Staff training on new security protocols and data handling: The human element is often a major vulnerability in data security. We provide comprehensive training for your staff on the new Dynamics 365 system, including best practices for data handling, new security protocols, and how to recognise and respond to potential threats. Well-trained staff are your first line of defence.
- Clear data governance policies and compliance with regulations: We assist you in establishing clear data governance policies within your new CRM, ensuring that data quality and security are maintained long-term. This also reinforces compliance with relevant data protection regulations, such as the Australian Privacy Principles.
- Transparent communication with your customers about data protection: Maintaining customer trust is paramount. We advise on how to communicate transparently with your customers about the CRM migration and the robust measures taken to protect their data. Proactive communication about security measures, including encryption standards and compliance, can significantly reassure your customers.
- BeyondCRM supports your team with ongoing CRM optimisation and governance: Our commitment extends beyond migration. We offer ongoing support and CRM optimisation services to help your team maximise the value of Dynamics 365 and ensure continued data security and compliance.
Explore our CRM upgrade services
Common Pitfalls in CRM Data Migration
Even with careful planning, CRM data migrations can encounter challenges. Understanding these common pitfalls helps us proactively mitigate risks and ensure a smoother process.
- Skipping data quality checks, leading to errors or exposure: One of the most significant risks is migrating dirty data. As the saying goes, “garbage in, garbage out.” Poor data quality can lead to incorrect reporting, flawed customer insights, and even expose sensitive information if not properly cleaned and validated. It can also cause mapping errors that compromise data integrity.
- Inadequate access controls, risking unauthorised data access: Without stringent role-based access controls and multi-factor authentication, there’s a heightened risk of unauthorised individuals accessing sensitive customer data during or after the migration. This can lead to data breaches and severe reputational damage.
- Overlooking compliance requirements for your industry: Different industries and regions have specific data protection regulations. Failing to account for these during migration can result in hefty fines and legal repercussions. For example, ignoring the Australian Privacy Principles for businesses in Australia is a critical oversight.
- Failing to train staff on new processes and security measures: Even the most secure system can be compromised by human error. If staff are not adequately trained on the new CRM’s features, data handling protocols, and security best practices, they can inadvertently create vulnerabilities.
- Not having a clear rollback or recovery plan: Despite best efforts, unforeseen issues can arise. Without a well-defined backup, rollback, and recovery plan, a failed migration can lead to significant data loss and prolonged business disruption. This underscores the importance of thorough data backups before any migration begins.
BeyondCRM helps you avoid these pitfalls with a structured, expert-led approach. We leverage our experience and Microsoft Dynamics 365 best practices to steer these complexities, ensuring your migration is successful and secure.
FAQs
What are the biggest security risks during a CRM data migration?
Unsecured data transfer, data corruption, unauthorised access, and compliance breaches are common risks. BeyondCRM uses proven controls to minimise these threats through encryption, access management, and rigorous validation.
How does data quality affect a secure CRM data migration?
Poor data quality can cause mapping errors and expose sensitive information. BeyondCRM’s process includes thorough data cleansing and validation to ensure accuracy and security, preventing the migration of flawed or outdated records.
How long does a secure CRM migration take?
The timeline depends on your data’s size and complexity, as well as the level of customisation required. BeyondCRM works with you to plan an efficient, secure migration custom to your needs, typically ranging from a few weeks for simpler migrations to several months for highly complex enterprise solutions.
What makes BeyondCRM’s approach to data migration secure?
We combine industry best practices, Microsoft Dynamics 365’s robust security features, and our own proven methodology to protect your data at every stage. This includes meticulous planning, advanced encryption, stringent access controls, extensive testing, and ongoing support for data governance.
How does BeyondCRM ensure compliance with Australian data privacy laws during migration?
We integrate compliance with Australian Privacy Principles (APPs) into our planning and execution. This involves identifying sensitive data, implementing appropriate security measures, and ensuring data handling practices align with regulatory requirements specific to your industry and location in Australia.
Conclusion
A fortress-like approach to CRM data migration protects your most valuable asset—customer data—at every step.
By partnering with BeyondCRM, you gain a trusted Microsoft Dynamics 365 expert who guides you through planning, execution, and ongoing governance. We are committed to delivering a secure, efficient, and compliant migration that empowers your business with a powerful new CRM solution.
Ready to secure your CRM migration?
Contact BeyondCRM to discuss your project, or explore our full range of CRM setup, upgrade, and optimisation services.


